Libraries.io
NewReleases
Banditore
Vulmon Alerts
Sibbell
pyup.io
ReleaseBell
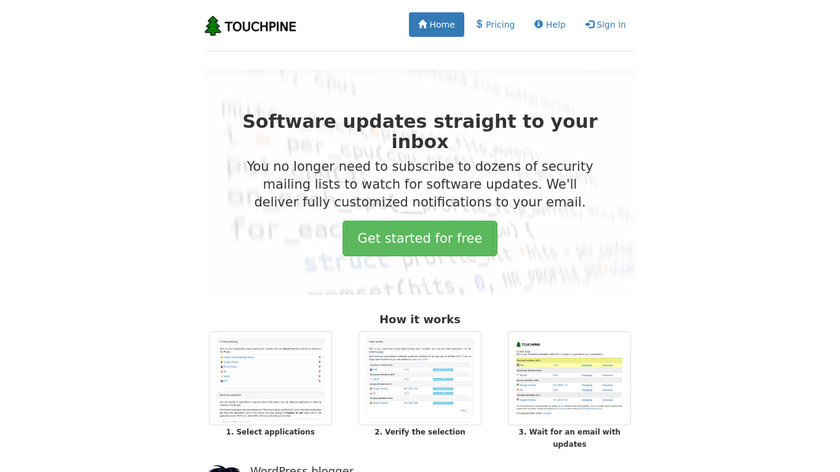
Software updates under control
Snyk
Aikido Security
WhiteSource Renovate
SonarQube
Vulmon Alerts
Greenkeeper
Depfu
Automated dependency updates for your Ruby, Python, JavaScript, PHP, .NET, Go, Elixir, Rust, Java and Elm.
Which is more popular?
Based on our record, Dependabot seems to be a lot more popular than Touchpine. While we know about 14 links to Dependabot, we've tracked only 1 mention of Touchpine.
Website, pricing, platforms and company facts side by side.
|
|
|
|
|---|---|---|
| Website | touchpine.com | dependabot.com |
| Pricing | ||
| Listed in |
What each product offers, as listed by its team.


Possible disadvantages
An editorial look at what each product does well and who it suits.


No analysis of Touchpine yet.
Overall verdict
Why this product is good
Recommended for
How often each product is chosen within a category, 0–100% relative to the other.


Share your experience with using Touchpine and Dependabot. For example, how are they different and which one is better?
External articles and on-site reviews we used to compare the two products.


We have no reviews of Touchpine yet. Be the first one to post
Luckily, we’ve been able to use GitHub bots to automate dependency management to an extent with solutions like Dependabot and GreenKeeper.
Recommendations tracked on public social media and blogs since March 2021.


You can also use version monitoring service like Touchpine (paid service) which can monitor RouterOS in one place together with other software you're interested in. Source: about 4 years ago
Additionally, while tools like Dependabot already automate dependency updates, this solution offers something a bit different: it doesn’t stop at upgrading libraries—it helps you deal with the consequences of those upgrades by offering... - Source: dev.to / over 1 year ago
GitHub integrated security scanning for vulnerabilities in their repositories. When they find a vulnerability that is solved in a newer version, they file a Pull Request with the suggested fix. This is done by a tool called Dependabot. - Source: dev.to / about 4 years ago
Dependabot provides a way to keep your dependencies up to date. Depending on the configuration, it checks your dependency files for outdated dependencies and opens PRs individually. Then based on requirement PRs can be reviewed and merged. - Source: dev.to / almost 5 years ago
When comparing Touchpine and Dependabot, you can also consider the following products.

:books: The Open Source Discovery Service. Contribute to librariesio/libraries.io development by creating an account on GitHub.
Compare Libraries.io to Touchpine or Dependabot:

Snyk helps you use open source and stay secure. Continuously find and fix vulnerabilities for npm, Maven, NuGet, RubyGems, PyPI and much more.
Compare Snyk to Touchpine or Dependabot:

Stop wasting your time checking manually if some piece of software is updated. Get Email, Slack, Telegram, Discord, Hangouts Chat, Microsoft Teams, Mattermost, Rocket.Chat, or Webhooks notifications.
Compare NewReleases to Touchpine or Dependabot:

Secure your code, cloud, and runtime in one central system. Find and fix vulnerabilities fast and automatically.
Compare Aikido Security to Touchpine or Dependabot:

Banditore retrieves new releases from your GitHub starred repositories and put them in a RSS feed, just for you.
Compare Banditore to Touchpine or Dependabot:

Automate your dependency updates
Compare WhiteSource Renovate to Touchpine or Dependabot: