Software Alternatives & Startups

Splunk Enterprise VS Android SysLog

Compare Splunk Enterprise VS Android SysLog and see what are their differences
Splunk Enterprise

Splunk Enteprise is the fastest way to aggregate, analyze and get answers from your machine data with the help machine learning and real-time visibility.
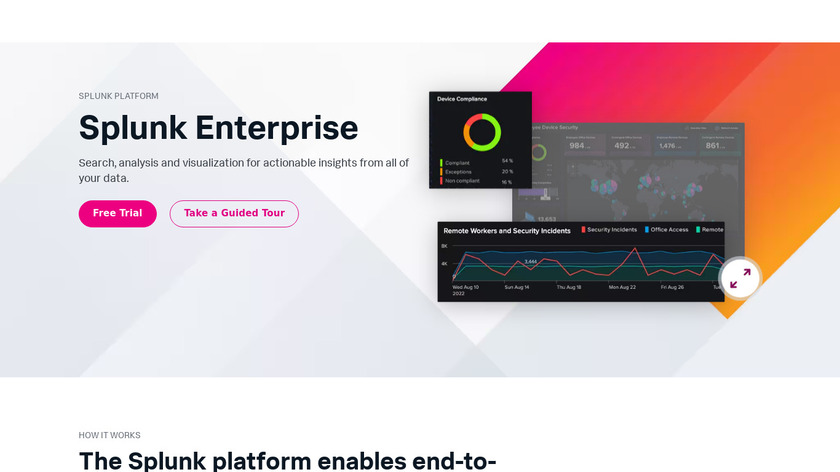
Splunk Enterprise Landing page
Rating
0 reviews
Android SysLog

This is a simple application that records various log types, and compresses them as a zip file. The logs are saved in the application's private cache directory named by the date and time.

No screenshot yet
Rating
0 reviews

Which is more popular?

Monitoring Tools popularity
97% vs 3%
alternatives listed
240+ vs 12

Base details

Website, pricing, platforms and company facts side by side.

Splunk Enterprise
Android SysLog
Website splunk.com github.com
Listed in

Features and specs

What each product offers, as listed by its team.

Splunk Enterprise 7 features
Android SysLog 5 features
  • Scalability
    Splunk Enterprise is designed to handle large volumes of data from different sources, making it suitable for enterprises of all sizes.
  • Real-time monitoring
    It offers real-time data analysis and monitoring, helping organizations to detect and respond to issues as they happen.
  • Custom dashboards
    Users can create custom dashboards aligned with their specific needs, offering flexibility in data visualization.
  • Data Integration
    Splunk supports integration with a wide range of data sources including logs, metrics, and events from various applications and systems.
  • Advanced Analytics
    It provides advanced analytics capabilities, including machine learning models to recognize patterns and anomalies in the data.
  • User Community and Support
    Splunk has a large user community and extensive documentation, helping users to find solutions and best practices more effectively.
  • Robust Security
    It offers multiple security features including data encryption, user authentication, and access control to protect sensitive information.

Possible disadvantages

  • Cost
    Splunk Enterprise can be expensive, especially for smaller organizations, because of its licensing and hardware requirements.
  • Complexity
    Setting up and managing Splunk can be complex and might require specialized knowledge and training.
  • High Resource Consumption
    The platform can be resource-intensive, requiring significant compute and storage capacity depending on data volume.
  • Overhead for Small Deployments
    For smaller deployments, the comprehensive capabilities of Splunk can be overkill, leading to unnecessary overhead.
  • Customization Learning Curve
    While custom dashboards are a strong feature, they can have a steep learning curve, requiring time and expertise to fully utilize.
  • Search Performance
    The search performance can degrade as the volume of data increases, necessitating additional tuning and optimization.
  • Open Source
    Android SysLog is open source, allowing developers to review, modify, and contribute to the code, leading to increased transparency and potential for community-driven improvements.
  • Log Access
    The tool provides access to system logs on Android devices, which can be invaluable for debugging and monitoring app performance or system behavior.
  • User-Friendly
    Android SysLog offers an easy-to-use interface that simplifies the process of retrieving and managing logs, making it accessible even for users with limited technical expertise.
  • Customization
    The tool allows for customization and configuration tailored to specific logging needs, offering flexibility for different use cases.
  • Community Support
    Being a well-known tool in the developer community, it often benefits from community support, where users can find help and share solutions.

Possible disadvantages

  • Limited Functionality
    Compared to more comprehensive monitoring solutions, Android SysLog may have limited features, focusing primarily on basic log retrieval and display.
  • Device Compatibility
    Compatibility with some devices or versions of Android may be limited, which could restrict its usability across different platforms.
  • Manual Configuration
    Setting up and configuring the application might require manual intervention, which can be cumbersome and technical for some users.
  • Security Concerns
    Handling system logs might raise security concerns, especially if sensitive information is not adequately protected or managed.
  • Dependency on Permissions
    To access system logs, the app might require extensive permissions, which could pose privacy concerns or create obstacles in environments with restricted access.

Analysis

An editorial look at what each product does well and who it suits.

Splunk Enterprise
Android SysLog

Overall verdict

  • Yes, Splunk Enterprise is considered a good choice for businesses aiming to enhance their data analytics capabilities. It is well-suited for enterprises that need to handle large-scale data analysis, monitor performance, and troubleshoot issues effectively.

Why this product is good

  • Splunk Enterprise is highly regarded for its ability to index, search, and analyze vast amounts of machine-generated data in real-time. It offers powerful visualization tools, extensive data integration capabilities, and robust security features. This makes it ideal for organizations looking to derive actionable insights and improve operational efficiency.

Recommended for

    Splunk Enterprise is recommended for IT and security teams, data analysts, and businesses that require advanced log management, real-time data processing, and comprehensive reporting tools. It is particularly valuable for industries such as finance, healthcare, retail, and telecommunications where data-driven decision-making is crucial.

Overall verdict

  • Android SysLog is a useful open-source utility for developers who need to capture and inspect device log output (logcat) directly on Android devices, offering a lightweight and free way to debug apps in the field.

Why this product is good

  • It's open source and free, so you can inspect and modify the code as needed
  • Allows viewing system and application logs directly on the device without a connected computer
  • Helpful for debugging apps in real-world conditions where a development machine isn't available
  • Community-driven on GitHub, meaning issues and improvements can be contributed by users

Recommended for

  • Android developers who need on-device log inspection
  • QA testers debugging issues in the field without ADB access
  • Open-source enthusiasts who want a transparent, modifiable logging tool
  • Anyone troubleshooting app crashes or system behavior on Android

Videos

Walkthroughs and reviews on video.

Splunk Enterprise 1 video + Add
Android SysLog 0 videos + Add

Webinar: Splunk Enterprise Security (Splunk ES)

No Android SysLog videos yet. You could help us improve this page by suggesting one.

Category popularity

How often each product is chosen within a category, 0–100% relative to the other.

Score bands 0–20 21–40 41–50 51–60 61–100
Splunk Enterprise
Android SysLog
97% 97%
3% 3%
0% 0%
100% 100%
100% 100%
0% 0%
0% 0%
100% 100%

User comments

Share your experience with using Splunk Enterprise and Android SysLog. For example, how are they different and which one is better?

Log in or Post with

Alternatives to Splunk Enterprise and Android SysLog

When comparing Splunk Enterprise and Android SysLog, you can also consider the following products.