Software Alternatives & Startups

SolarWinds Patch Manager VS Penetrify.cloud

Compare SolarWinds Patch Manager VS Penetrify.cloud and see what are their differences
SolarWinds Patch Manager

SolarWinds Patch Manager is an intuitive patch management software for quickly addressing software vulnerabilities.
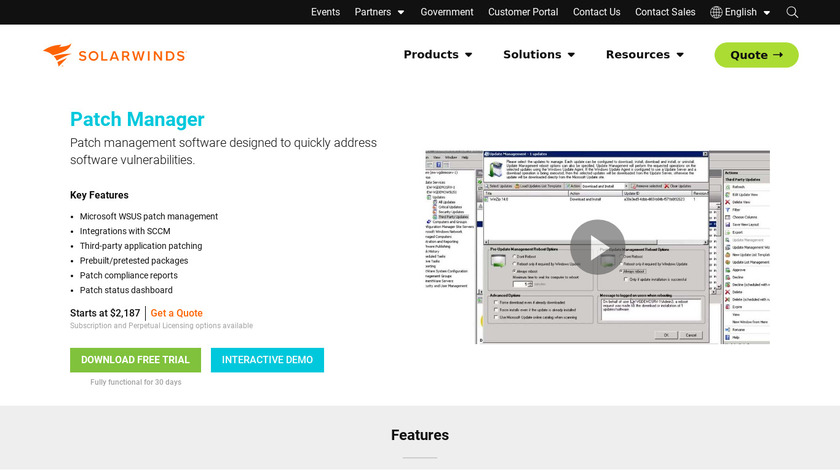
SolarWinds Patch Manager Landing page
Rating
0 reviews
Penetrify.cloud

Autonomous AI penetration testing, on every deploy

Penetrify.cloud Dashboard penetrify.cloud
Rating
0 reviews
Pricing
Paid $100 / Monthly (1 penetration test per month)

Which is more popular?

Monitoring Tools popularity
100% vs 0%
alternatives listed
150 vs 17

Base details

Website, pricing, platforms and company facts side by side.

SolarWinds Patch Manager
Penetrify.cloud
Website solarwinds.com penetrify.cloud
Pricing
Paid $100 / Monthly (1 penetration test per month) Official pricing
Platforms
Web SaaS Cloud
Company Startup from the Czech Republic · 10 - 19 employees · 2025
Listed in

About SolarWinds Patch Manager and Penetrify.cloud

In their own words, as submitted to SaaSHub.

SolarWinds Patch Manager
Penetrify.cloud

No description of SolarWinds Patch Manager yet.

Penetrify replaces the once-a-year manual penetration test with an autonomous AI red team that runs whenever you deploy. Point it at a target and the agent handles the whole engagement itself - reconnaissance, authentication and authorization testing, exploitation, and multi-step attack chaining...

Read more about Penetrify.cloud

Features and specs

What each product offers, as listed by its team.

SolarWinds Patch Manager 5 features
Penetrify.cloud 2 features
  • Comprehensive Patch Management
    SolarWinds Patch Manager offers a wide range of patch management capabilities for both Microsoft and third-party applications, ensuring that systems stay updated and secure against vulnerabilities.
  • Automated Patching
    The automation features allow for streamlined scheduling and deployment of patches, reducing the manual workload and risk of human error in patch management processes.
  • Integration with WSUS and SCCM
    SolarWinds Patch Manager integrates seamlessly with Microsoft WSUS and SCCM, enabling enhanced control over patch management processes and leveraging existing infrastructure.
  • Detailed Reporting and Compliance
    The tool provides comprehensive reporting and compliance features, offering insights into the patch status and compliance levels across the organization.
  • User-Friendly Interface
    The interface is designed to be intuitive and easy to navigate, facilitating quick access to necessary tools and information for IT administrators.

Possible disadvantages

  • Cost Considerations
    SolarWinds Patch Manager can be costly for small to medium-sized businesses, potentially limiting access for organizations with tighter IT budgets.
  • Complex Initial Setup
    The initial setup and configuration process can be complex and requires adequate expertise, which may be challenging for teams with limited experience.
  • Third-Party Vendor Support
    While it supports a wide range of third-party applications, there may still be some vendors whose patches are not supported, requiring manual handling.
  • Performance Overhead
    The software might introduce performance overhead on systems, particularly during scan and deployment phases, potentially impacting system responsiveness.
  • Limited Mobile Device Support
    SolarWinds Patch Manager is primarily designed for desktop and server environments, with limited capabilities for managing patches on mobile devices.
  • Fully autonomous
    runs from a URL, no operator
  • Exploits & chains vulnerabilities
    proof, not just alerts

Analysis

An editorial look at what each product does well and who it suits.

SolarWinds Patch Manager
Penetrify.cloud

No analysis of SolarWinds Patch Manager yet.

Overall verdict

  • I don't have verified, specific information about Penetrify.cloud, as it appears to be a lesser-known or possibly new service without substantial independent reviews, security audits, or established reputation data available to me. Before using it, especially for security/penetration testing purposes, thorough independent research is strongly recommended.

Why this product is good

  • Limited public information or third-party reviews are available to verify claims of quality or reliability
  • No verifiable track record, certifications, or client testimonials could be confirmed
  • Security and penetration testing tools require high trust, and unverified providers carry inherent risk
  • Domain and branding suggest a niche cybersecurity tool, but legitimacy and effectiveness are unconfirmed

Recommended for

  • Not recommended without independent verification
  • Users should first check for company transparency, contact information, and business registration
  • Security professionals should look for peer reviews, case studies, or industry recognition before adoption
  • Consider established, well-reviewed alternatives in the penetration testing space unless you can independently verify this service's credibility and safety

Videos

Walkthroughs and reviews on video.

SolarWinds Patch Manager 3 videos + Add
Penetrify.cloud 1 video + Add

Solarwinds Patch Manager Demo

More videos

  • Review - Introduction to SolarWinds Patch Manager
  • Review - SolarWinds Lab Bits: A Brief SolarWinds Patch Manager Overview

Penetrify.cloud: Create and Run a Security Test for a New Application

Category popularity

How often each product is chosen within a category, 0–100% relative to the other.

Score bands 0–20 21–40 41–50 51–60 61–100
SolarWinds Patch Manager
Penetrify.cloud
100% 100%
0% 0%
0% 0%
100% 100%
100% 100%
0% 0%
0% 0%
100% 100%

Questions & Answers

As answered by people managing SolarWinds Patch Manager and Penetrify.cloud.

What makes your product unique?

Penetrify.cloud's answer:

Most tools scan - they flag patterns that might be vulnerable. Penetrify exploits: an autonomous AI agent actually attacks the application, chains weaknesses into multi-step attack paths, and proves real impact, the way a human pentester would. It does this from just a URL, with no operator or security expertise needed, and runs continuously on every deploy through your CI/CD pipeline. The result is penetration-test depth - including authorization, IDOR, and business-logic flaws that scanners miss - delivered as an always-on SaaS instead of a once-a-year engagement.

Why should a person choose your product over its competitors?

Penetrify.cloud's answer:

  • vs. manual penetration testing: results in minutes instead of 1–3 weeks, from $100/month instead of $10,000–$50,000 per engagement, and continuous on every release instead of once or twice a year.
  • vs. DAST scanners (Burp Suite, Acunetix, OWASP ZAP): Penetrify exploits and chains vulnerabilities rather than only detecting known signatures, so it catches broken access control, IDOR, SSRF, and business-logic flaws those tools typically miss - and it's fully autonomous, requiring no manual operator.
  • vs. other AI security tools: true end-to-end autonomy (URL in, exploit-proven report out), native CI/CD integration, and developer-focused reports with reproduction steps and remediation.

How would you describe the primary audience of your product?

Penetrify.cloud's answer:

Development teams, startups, founders, and SMBs - fast-shipping teams that need continuous security coverage but don't have the budget for repeated manual pentests or an in-house offensive-security specialist. Also DevSecOps engineers who want a real penetration test wired into the build pipeline rather than a periodic audit.

What's the story behind your product?

Penetrify.cloud's answer:

Penetrify was founded in 2025 in Brno, Czech Republic, by Viktor Bulanek (MSc IT Security, 20+ years in security, four-time CTO). After years building and securing production systems, he kept seeing the same gap: startups were priced out of $10k–$50k manual pentests and stuck with once-a-year testing that couldn't keep up with weekly deploys. So the team built an autonomous AI agent that runs the same methodology a senior security engineer would - continuously, and at a price a side project can justify. Penetrify is operated by Algofy s.r.o.

Which are the primary technologies used for building your product?

Penetrify.cloud's answer:

Penetrify runs on AWS serverless infrastructure (Lambda, containerized agents, S3, CloudFront). The autonomous testing agents are powered by frontier large language models, including Anthropic's Claude. The backend is a Python/FastAPI API; the web app is built with React and TypeScript.

Who are some of the biggest customers of your product?

Penetrify.cloud's answer:

As a security vendor we keep our customer list confidential - clients generally prefer not to publicize who runs their penetration testing. Penetrify is used primarily by startups, SaaS companies, and software development teams that ship frequently and need continuous security coverage.

User comments

Share your experience with using SolarWinds Patch Manager and Penetrify.cloud. For example, how are they different and which one is better?

Log in or Post with

Alternatives to SolarWinds Patch Manager and Penetrify.cloud

When comparing SolarWinds Patch Manager and Penetrify.cloud, you can also consider the following products.