Software Alternatives & Startups

MicroFocus DevInspect VS ModSecurity

Compare MicroFocus DevInspect VS ModSecurity and see what are their differences
MicroFocus DevInspect

DevInspect is a secure coding tool designed specifically for developers who need agile development but cannot compromise on application security.
MicroFocus DevInspect Landing page
Rating
0 reviews
ModSecurity

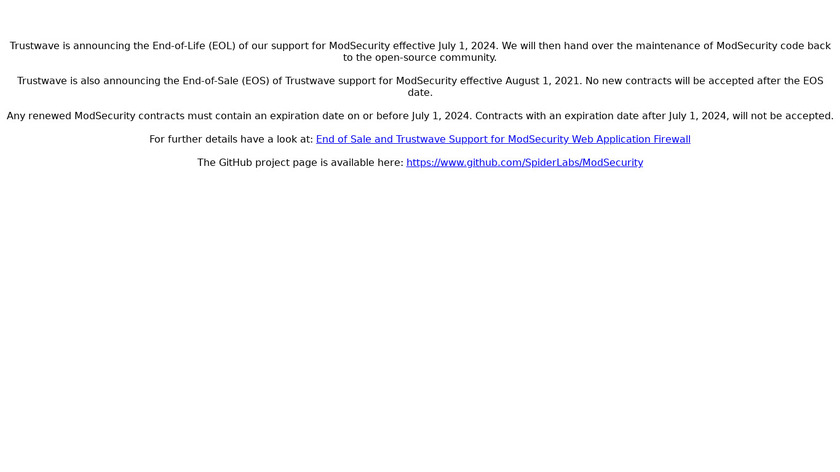
ModSecurity is an Open Source web application firewall developed by Trustwave's SpiderLabs.
ModSecurity Landing page
Rating
0 reviews
Pricing
Open source

Which is more popular?

Security & Privacy popularity
47% vs 53%
alternatives listed
38 vs 110

Base details

Website, pricing, platforms and company facts side by side.

MicroFocus DevInspect
ModSecurity
Website microfocus.com modsecurity.org
Pricing
Open source
Listed in

Features and specs

What each product offers, as listed by its team.

MicroFocus DevInspect 5 features
ModSecurity 6 features
  • Comprehensive Security Testing
    DevInspect offers a wide range of security testing features that can help identify vulnerabilities in web applications, ensuring a thorough assessment of potential security risks.
  • Integration with Development Tools
    The product can be seamlessly integrated with various development environments and CI/CD pipelines, enhancing workflow efficiency by allowing developers to identify and fix security issues early in the development cycle.
  • Ease of Use
    Designed with a user-friendly interface, DevInspect caters to both security professionals and developers, making it accessible to users with varying levels of expertise.
  • Regular Updates
    Micro Focus provides frequent updates and support to ensure DevInspect is equipped to handle the latest security vulnerabilities and threats.
  • Detailed Reporting
    Offers comprehensive reporting features that provide detailed insights into security flaws and recommendations for remediation, which is crucial for understanding and addressing vulnerabilities effectively.

Possible disadvantages

  • Complexity in Setup
    The initial setup and configuration of DevInspect may be complex and time-consuming, potentially requiring significant technical expertise or support from Micro Focus.
  • Cost
    As a high-end security solution, DevInspect can be expensive, which might be a constraint for smaller organizations or those with limited budgets.
  • Learning Curve
    While the interface is user-friendly, mastering all the features and functionalities may require considerable time and training, particularly for users new to application security.
  • Resource Intensive
    Running comprehensive security tests can be resource-intensive, potentially impacting system performance and requiring robust infrastructure to handle extensive analyses efficiently.
  • Limited Language Support
    DevInspect may have limitations regarding the range of programming languages and technologies it supports, which could be a drawback for organizations using less common technologies.
  • Open Source
    ModSecurity is open-source, which means it's freely available for use and modification. This allows for transparency and community-driven improvements.
  • Flexibility
    ModSecurity supports a wide variety of configurations and rules, allowing it to be tailored to specific needs and environments.
  • Comprehensive Protection
    ModSecurity can protect against a wide range of threats including SQL injection, cross-site scripting (XSS), and other common web vulnerabilities.
  • Cross-Platform
    ModSecurity can be integrated with various web servers including Apache, Nginx, and IIS, providing versatility across different platforms.
  • Ongoing Development
    Being widely adopted, ModSecurity benefits from continuous updates and active community and vendor support, ensuring it remains effective against new threats.
  • Event Logging
    ModSecurity offers detailed logging capabilities, which can be crucial for auditing and forensic analysis.

Possible disadvantages

  • Complex Configuration
    Setting up and configuring ModSecurity can be complex and time-consuming, requiring a good understanding of web security and the server environment.
  • Performance Overhead
    ModSecurity can introduce performance overhead, particularly if the rule sets are extensive and complex, potentially impacting web server performance.
  • False Positives
    There can be a significant number of false positives, where legitimate traffic is incorrectly flagged as malicious, which requires continuous tuning and refinement.
  • Limited GUI
    ModSecurity lacks a robust graphical user interface (GUI) for management, which means most configuration has to be done through command-line or manual editing of configuration files.
  • Learning Curve
    Due to its powerful and complex nature, there is a steep learning curve associated with effectively utilizing ModSecurity.

Analysis

An editorial look at what each product does well and who it suits.

MicroFocus DevInspect
ModSecurity

No analysis of MicroFocus DevInspect yet.

Overall verdict

  • Yes, ModSecurity is generally considered a good option for web application security.

Why this product is good

  • ModSecurity is an open-source web application firewall (WAF) that provides powerful protection against a variety of web threats, including SQL injection, cross-site scripting (XSS), and other common vulnerabilities.
  • It offers a flexible rule engine that allows users to implement custom security rules tailored to their specific needs, enhancing its adaptability and effectiveness.
  • ModSecurity has a strong community of users and developers that contribute to its development and offer support and resources, ensuring continuous improvements and updates.
  • The tool is highly configurable and can be integrated with Apache, Nginx, and IIS servers, making it a versatile option for different server environments.
  • Built with performance in mind, ModSecurity enables comprehensive logging and monitoring capabilities, which are essential for threat analysis and incident response.

Recommended for

  • Organizations looking for a cost-effective and customizable solution to enhance their web application security.
  • Developers and system administrators who are comfortable configuring and maintaining open-source tools.
  • Businesses operating in environments that use Apache, Nginx, or IIS web servers.
  • Web applications that need to meet strict compliance and regulatory requirements concerning security and data protection.
  • Companies aiming to protect against the OWASP Top Ten security risks and other web vulnerabilities.

Videos

Walkthroughs and reviews on video.

MicroFocus DevInspect 0 videos + Add
ModSecurity 2 videos + Add

No MicroFocus DevInspect videos yet. You could help us improve this page by suggesting one.

Secure your Apps with NGINX and the ModSecurity WAF

More videos

Category popularity

How often each product is chosen within a category, 0–100% relative to the other.

Score bands 0–20 21–40 41–50 51–60 61–100
MicroFocus DevInspect
ModSecurity
47% 47%
53% 53%
11% 11%
89% 89%
100% 100%
0% 0%
0% 0%
100% 100%

User comments

Share your experience with using MicroFocus DevInspect and ModSecurity. For example, how are they different and which one is better?

Log in or Post with

Alternatives to MicroFocus DevInspect and ModSecurity

When comparing MicroFocus DevInspect and ModSecurity, you can also consider the following products.