Tailwind CSS
Windows95
Virtual Windows 98
Vast.ai
Geo Bootstrap
Webamp
UI Movement
A design system for building faithful recreations of old UIs
AttackForge
dradis
Faraday IDE
SysReptor
PentestReportAI
Cyver
Vulnsy
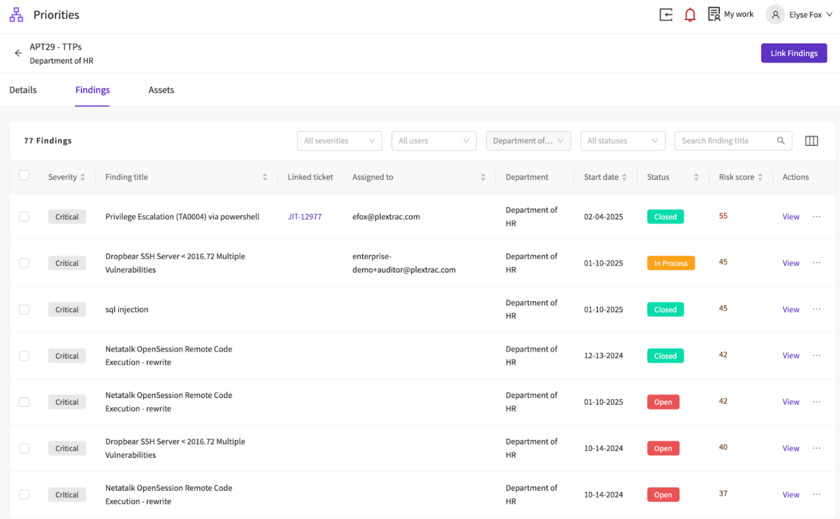
PlexTrac is the #1 AI-powered platform for pentest reporting and threat exposure management, helping cybersecurity teams efficiently address the most critical threats and vulnerabilities.
Which is more popular?
Based on our record, 98.css seems to be more popular. It has been mentioned 21 times since March 2021.
Website, pricing, platforms and company facts side by side.
|
|
|
|
|---|---|---|
| Website | jdan.github.io | plextrac.com |
| Pricing | ||
| Company | — | Startup from the United States · 250 - 499 employees · 2022 |
| Listed in |
In their own words, as submitted to SaaSHub.


No description of 98.css yet.
PlexTrac’s automated platform accelerates report writing and the findings handoff by enabling pentesters to reuse content, leverage over 25,000 pre-built findings writeups (CWEs, CVEs, and KEVs), customize templates without code, analyze data across sources, and streamline QA with Google-doc-like...
What each product offers, as listed by its team.


Possible disadvantages
Walkthroughs and reviews on video.
No 98.css videos yet. You could help us improve this page by suggesting one.
Create a Pentest Report in 5 Minutes or Less with PlexTrac — PlexTrac Demo
More videos
How often each product is chosen within a category, 0–100% relative to the other.


As answered by people managing 98.css and PlexTrac.
PlexTrac's answer:
PlexTrac is the only platform that bridges the gap between offensive and defensive security teams by bringing together pentest reporting, vulnerability management, and threat exposure tracking in one unified, workflow-driven platform.
Unlike traditional tools that just generate static reports or list findings, PlexTrac enables real-time collaboration, automated risk scoring, and continuous validation — helping teams move from findings to fixes faster.
PlexTrac's answer:
People choose PlexTrac because it:
Saves time — teams report saving 30–70% of the time previously spent on manual reporting and remediation tracking.
Centralizes security data — findings from scanners, pentests, bug bounty platforms, and red team ops are all in one place.
Prioritizes what matters — contextual risk scoring helps teams focus on the vulnerabilities that actually pose a business risk.
Enables automation — from report generation to ticketing workflows with Jira, ServiceNow, and more.
Works for both enterprises and MSSPs — with multi-tenant support, customizable templates, and powerful integrations.
Bottom line: PlexTrac turns vulnerability noise into actionable, trackable, and reportable outcomes.
PlexTrac's answer:
PlexTrac primarily serves:
Enterprise cybersecurity teams (especially blue and purple teams)
Red teams and penetration testers looking to streamline reporting and remediation
MSSPs who need a scalable platform to manage clients, reports, and workflows
CISOs and security leaders who want visibility into remediation progress and risk trends
These users are typically frustrated by manual workflows, fragmented tools, and poor collaboration across security functions.
PlexTrac's answer:
PlexTrac was founded by Dan DeCloss, a former red teamer and security leader, who experienced firsthand the pain of manual reporting, siloed data, and disconnected remediation workflows.
He built PlexTrac to bridge the communication gap between red and blue teams, helping security professionals work faster, collaborate better, and reduce real risk more efficiently.
Since its founding, PlexTrac has evolved from a better reporting tool to a comprehensive threat exposure management platform used by hundreds of security teams worldwide.
PlexTrac's answer:
Fortune 500 enterprises across finance, healthcare, and tech
Leading MSSPs and consultancies who deliver pentesting and security services at scale
Federal government agencies and defense contractors requiring compliance with frameworks like NIST and CMMC
Higher education institutions with active security testing programs
Share your experience with using 98.css and PlexTrac. For example, how are they different and which one is better?
Recommendations tracked on public social media and blogs since March 2021.


Wow it’s aggressively vibe coded. Nothing inherently wrong with that, but it looks a bit amateurish which is funny. I’m still waiting on 98.css to become the standard for vibe coded sites. You don’t have to read docs anyway if you’re... - Source: Hacker News / about 1 month ago
There's an entire lightweight CSS lib around the Win9x look as well: https://jdan.github.io/98.css/. - Source: Hacker News / 3 months ago
Nothing screams old school more than 98.css https://jdan.github.io/98.css/. - Source: Hacker News / 5 months ago
Tracking PlexTrac since Mar 2021.
When comparing 98.css and PlexTrac, you can also consider the following products.

A utility-first CSS framework for rapidly building custom user interfaces.
Compare Tailwind CSS to 98.css or PlexTrac:

AttackForge is the #1 Penetration Testing Management & Collaboration Platform for Enterprise. Bringing Security & Business Together On Your Pentesting Program.
Compare AttackForge to 98.css or PlexTrac:

Windows 95 in Electron. Runs on macOS, Linux, and Windows.
Compare Windows95 to 98.css or PlexTrac:

Dradis is the open-source reporting and collaboration tool for IT security professionals.
Compare dradis to 98.css or PlexTrac:

Collaborative Penetration Test and Vulnerability Management Platform that increases transparency...
Compare Faraday IDE to 98.css or PlexTrac: