-
The fully pluggable JavaScript code quality toolPricing:
- Open Source
- Customization - ESLint is highly customizable through configuration files, allowing developers to tailor the linting process to fit their specific coding standards and project requirements.
- Extensibility - With a wide range of plugins and the ability to write custom rules, ESLint can be extended to accommodate unique project needs or additional languages and frameworks.
- Community Support - ESLint has a large and active community, ensuring continuous improvement, frequent updates, and a wealth of shared knowledge and resources.
- Error Prevention - By statically analyzing code to catch potential errors and bad practices before runtime, ESLint helps improve code quality and reduce bugs.
- Consistency - Applying ESLint across a project ensures coding standards are maintained consistently, which is particularly beneficial for teams with multiple developers.
#Developer Tools #Code Coverage #Code Quality 301 social mentions
-
Measure helps mobile teams monitor and fix crashes, ANRs, bugs, and performance issues. The open source alternative to Firebase Crashlytics.Pricing:
- Open Source
- Freemium
- Free Trial
- $25 / Monthly (25GB of log/metric/ traces/session replay)
- Crash Reporting - Crashes and ANRs with symbolicated stacktraces, grouping and version impact
- Session Replay - Session Timeline replays every user action, screen, network call, log and system metric
- Performance Monitoring - Traces, app launch times, network latency and app health metrics per release
- Bug Reporting - Shake the device to file a bug, attached to the full session that led to it
- Network Monitoring - Request latency, status codes and failing endpoints, tied to the session
#Observability #APM #Error Monitoring Featured
-
SonarQube, a core component of the Sonar solution, is an open source, self-managed tool that systematically helps developers and organizations deliver Clean Code.Pricing:
- Open Source
- Freemium
- Free Trial
- $150 / Annually
- Comprehensive code analysis - SonarQube provides detailed insights into code quality by examining various metrics such as code smells, bugs, vulnerabilities, and duplications.
- Multi-language support - It supports a wide range of programming languages like Java, C#, JavaScript, TypeScript, Python, PHP, and many others, making it versatile for different projects.
- Continuous integration (CI) integration - SonarQube integrates seamlessly with CI tools like Jenkins, GitLab CI, and Azure DevOps, facilitating continuous code inspection.
- Customizable rules - Users can customize and extend the set of rules to fit specific project needs and coding standards.
- User-friendly interface - The platform offers an intuitive and easy-to-navigate web interface for analyzing and managing code quality issues.
#Open Source #Code Review #Developer Tools 1 social mentions
-
Automatically reviews code style, security, duplication, complexity, and coverage on every change while tracking code quality throughout your sprints.Pricing:
- Open Source
- Comprehensive Code Analysis - Codacy offers a wide array of static code analysis tools that can help identify many types of issues such as code complexity, security vulnerabilities, and code duplication.
- Supports Multiple Languages - Codacy supports a wide variety of programming languages including Java, JavaScript, Python, Ruby, and more. This makes it suitable for polyglot development teams.
- Integration with CI/CD Pipelines - Codacy integrates seamlessly with popular Continuous Integration/Continuous Deployment (CI/CD) tools like Jenkins, CircleCI, and Travis CI, enabling automated code reviews as part of the development workflow.
- Customizable Analysis - It allows teams to set custom quality and code style thresholds, ensuring that the code analysis process is tailored to meet the specific requirements of the project.
- Automated Pull Request Reviews - Codacy can automatically review pull requests and report issues as comments, helping developers identify problems before merging code changes.
#Code Coverage #Code Quality #Static Code Analysis 4 social mentions
-
Find and fix defects in your Java, C/C++ or C# open source project for free
- Comprehensive Analysis - Coverity Scan offers deep and comprehensive analysis of your codebase, enabling the detection of critical bugs and security vulnerabilities that might be missed by other tools.
- Wide Language Support - Coverity Scan supports a wide range of programming languages including C, C++, Java, JavaScript, and Python, making it versatile for various projects.
- Integration with Development Workflow - Seamlessly integrates with popular version control systems like GitHub, making it easy to incorporate into your existing development workflow.
- Actionable Reports - Provides detailed and actionable reports that help developers understand the root cause of issues and how to fix them efficiently.
- Free for Open Source - Available for free for open-source projects, making it an accessible tool for community-driven and non-commercial projects.
#Code Review #Developer Tools #Code Coverage 4 social mentions
-
The industry’s most comprehensive AppSec platform, Checkmarx One is fast, accurate, and accelerates your business.
- Comprehensive Coverage - Checkmarx provides extensive support for multiple programming languages and frameworks, allowing for a broad range of applications to be scanned.
- Integration Capabilities - The platform integrates well with various DevOps tools and CI/CD pipelines, making it easier to incorporate security checks into the software development lifecycle.
- Customization - Offers highly customizable rule sets that can be tailored to specific security requirements and coding standards of the organization.
- User-Friendly Interface - Features an intuitive and easy-to-navigate user interface that allows users to efficiently manage and analyze security vulnerabilities.
- Scalability - Designed to scale efficiently, Checkmarx can handle large codebases and multiple projects concurrently without significant performance degradation.
#Web Application Security #Code Review #Developer Tools 4 social mentions
-
Code Climate provides automated code review for your apps, letting you fix quality and security issues before they hit production. We check every commit, branch and pull request for changes in quality and potential vulnerabilities.Pricing:
- Open Source
- Automated Code Review - CodeClimate automatically analyzes code for quality, security, and performance issues, helping developers maintain high standards without manual intervention.
- Extensive Integrations - CodeClimate offers integrations with popular tools like GitHub, GitLab, Bitbucket, and CI/CD pipelines, making it easy to integrate into existing workflows.
- Detailed Reporting - Provides comprehensive reports that highlight code issues, test coverage, duplication, and complexity, enabling developers to quickly identify and address problems.
- Team Collaboration - Facilitates better team collaboration by offering features such as pull request reviews and comments, which help teams discuss and resolve code issues collaboratively.
- Customizable Quality Gates - Allows teams to set custom quality gates and thresholds, ensuring that only code meeting specific quality standards is allowed to pass.
#Code Review #Code Coverage #Code Quality 19 social mentions
-
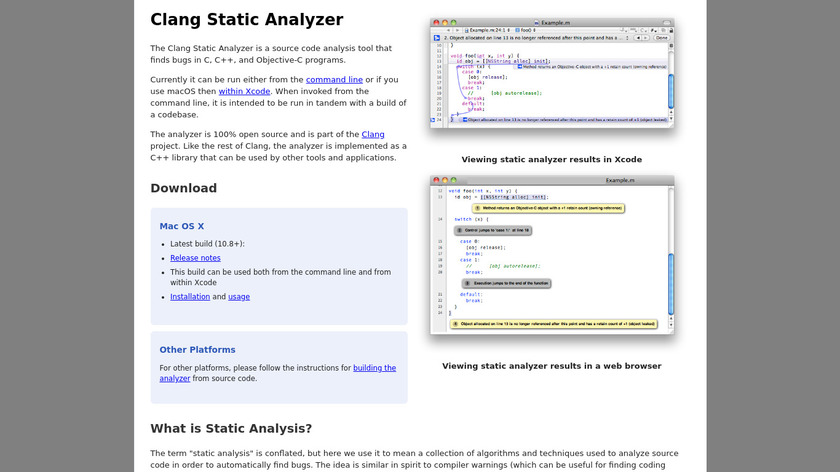
The Clang Static Analyzer is a source code analysis tool that finds bugs in C, C++, and Objective-C...
- Integration with Clang - The Clang Static Analyzer is built as part of the Clang project, ensuring seamless integration with the Clang compiler. This allows for easy adoption in projects that already use Clang for compiling, as there is no need for additional tooling setup.
- Open Source - Being an open-source tool, Clang Static Analyzer is freely available for anyone to use and modify. This encourages a community-driven approach to improvements and provides the flexibility to tailor the tool to specific needs.
- Path-sensitive Analysis - Clang Static Analyzer performs path-sensitive analysis, which means it evaluates different execution paths in the code to detect complex bugs that may only manifest under certain conditions.
- Deep C/C++ Support - As part of the LLVM project, Clang Static Analyzer offers robust support for C and C++ languages, leveraging the deep language understanding from the Clang front-end.
#Code Review #Code Coverage #Development 8 social mentions
-
Semgrep is a fast, open-source, static analysis tool for finding bugs and enforcing code standards at editor, commit, and CI time.Pricing:
- Open Source
- Easy to Use - Semgrep offers a straightforward setup and simple syntax, making it easy for developers to start using it for static code analysis without extensive configuration.
- Language Support - It supports a wide range of programming languages, including popular ones like Python, JavaScript, Java, and more, making it versatile for different codebases.
- Customizable Rules - Users can create custom rules tailored to their specific codebase needs, allowing for more control and precision over code analysis.
- Real-time Analysis - Semgrep can be integrated into CI/CD pipelines, providing real-time feedback on code submissions and helping to catch issues early in the development process.
- Open Source - Being open source, it allows for community contributions and transparency, enabling users to understand and trust the tool more deeply.
#Developer Tools #Code Coverage #Code Quality 26 social mentions
-
Pylint is a Python source code analyzer which looks for programming errors.
- Extensive Error Checking - PyLint provides comprehensive checks for errors in Python code, including syntax errors, structural problems, and more complex issues like unused variables and undefined names.
- Customizability - PyLint allows users to configure which types of errors and warnings they want to check for through configuration files, making it adaptable to different coding standards and preferences.
- Integration with Development Tools - PyLint can be integrated with various IDEs and editors such as Visual Studio Code, PyCharm, and more, enhancing the development workflow by providing real-time feedback.
- Code Quality Metrics - It offers additional metrics and ratings for code quality, helping developers understand the complexity and maintainability of their code.
- Code Refactoring Support - PyLint suggests specific code improvements and refactorings, which can enhance the readability and performance of the code.
#Code Review #Developer Tools #Code Coverage 13 social mentions
-
Capture website screenshots, render HTML/CSS, or create templated graphics. Render images or PDFs. Use MCP with AI, no-code automation, or the REST API. No browsers needed.Pricing:
- Freemium
- $14 / Monthly
- Ease of Use - The API allows users to convert HTML/CSS content to images with minimal code, making it accessible for developers.
- Customization - Users can have full control over the appearance of the generated images through HTML and CSS, enabling highly customizable output.
- Efficiency - The service automates the image generation process, allowing for quick and efficient conversion that saves development time.
- Scalability - The API can handle a large number of requests, making it suitable for applications that need to generate many images dynamically.
- Reusable Templates - Save a design, then generate new images by passing in text, images, and other values.
#HTML To Image #Website Screenshots #Image Generation API Featured
Top 9 Code Analysis Products in Code Quality
The best Code Analysis Products within the Code Quality category - based on our collection of reviews & verified products.
Sponsored products