Software Alternatives & Startups

DeepSource VS Dependabot

Compare DeepSource VS Dependabot and see what are their differences
DeepSource

Automated code reviews with static analysis.
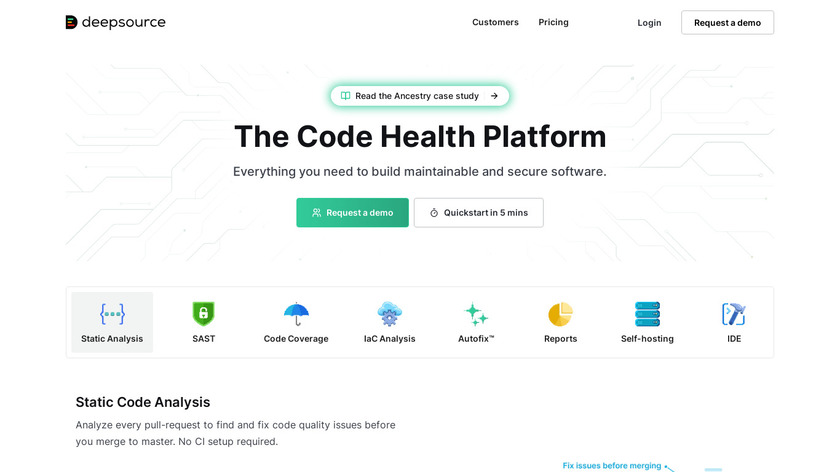
DeepSource Landing page
Rating
0 reviews
Dependabot

Automated dependency updates for your Ruby, Python, JavaScript, PHP, .NET, Go, Elixir, Rust, Java and Elm.
Dependabot Landing page
Rating
0 reviews
Note: These products don't have any matching categories. If you think this is a mistake, please edit the details of one of the products and suggest appropriate categories.

Which is more popular?

DeepSource might be a bit more popular than Dependabot. We know about 16 links to it since March 2021 and only 14 links to Dependabot.

social mentions
16 vs 14
Developer Tools popularity
74% vs 26%
alternatives listed
171 vs 95

Base details

Website, pricing, platforms and company facts side by side.

DeepSource
Dependabot
Website deepsource.com dependabot.com
Pricing
Company 2018
Listed in

About DeepSource and Dependabot

In their own words, as submitted to SaaSHub.

DeepSource
Dependabot

DeepSource helps you automatically find and fix issues in your code during code reviews, such as bug risks, anti-patterns, performance issues, and security flaws. It takes less than 5 minutes to set up with your Bitbucket, GitHub, or GitLab account. It works for Python, Go, Ruby, Java, and...

Read more about DeepSource

No description of Dependabot yet.

Features and specs

What each product offers, as listed by its team.

DeepSource 5 features
Dependabot 5 features
  • Automated Code Review
    DeepSource offers automated code review that helps developers quickly identify and fix issues in their code, improving overall code quality and reducing time spent on manual reviews.
  • Wide Language Support
    It supports a diverse set of programming languages, including Python, JavaScript, Ruby, and more, making it versatile for teams that work with multiple technologies.
  • Security Analysis
    DeepSource provides security checks that can detect vulnerabilities in the code, helping to ensure that applications are more secure against attacks.
  • Continuous Integration
    Its integration with popular CI/CD tools allows for seamless incorporation into the development pipeline, ensuring continuous code quality checks.
  • Developer Centric
    Designed with developer productivity in mind, it offers actionable insights and suggestions on how to fix code issues, facilitating faster resolution and learning.

Possible disadvantages

  • Limited Free Tier
    The free tier of DeepSource might be limited in features and capabilities, which can be a drawback for smaller teams or individual developers who may require more comprehensive functionality.
  • Learning Curve
    New users might experience a learning curve when getting acquainted with the tool, especially if they are less familiar with automated code analysis.
  • Customization Constraints
    While DeepSource provides customizable features, there may be constraints and limitations that affect highly specific or niche requirements.
  • Integration Complexity
    For some projects, integrating DeepSource into existing workflows may be complex and require additional setup and maintenance efforts.
  • Overwhelming Feedback
    The volume of feedback and suggestions provided can be overwhelming, particularly for large codebases, possibly requiring significant time and effort to address all issues.
  • Automated Dependency Updates
    Dependabot automatically scans your project for outdated dependencies and creates pull requests to update them, saving time and effort.
  • Security Vulnerability Alerts
    Dependabot identifies and alerts you to security vulnerabilities in your dependencies, providing fixes to enhance the security of your application.
  • Customizable Configuration
    Users can configure Dependabot's update frequency, dependency types (production, development), and even filter by specific packages or ecosystems.
  • Integration with CI/CD
    Integrates seamlessly with continuous integration and continuous deployment (CI/CD) pipelines, enabling automated testing of dependency updates.
  • Ease of Use
    Dependabot is easy to set up and integrates directly within GitHub, making it convenient for developers already using the platform.

Possible disadvantages

  • Potential Overwhelm from Updates
    Frequent updates may overwhelm developers with too many pull requests, making it hard to keep up, especially in larger projects.
  • Merge Conflicts
    Automated pull requests may occasionally cause merge conflicts, requiring manual intervention to resolve.
  • Limited Support for Private Repositories
    Dependabot's functionality for private repositories may sometimes be limited without appropriate permissions or configurations.
  • Performance Impact
    Dependabot's scanning and update activities may impact the performance of large repositories, potentially slowing down other operations.
  • Reliance on GitHub
    Being a GitHub-native tool, Dependabot's features are tightly coupled with GitHub, potentially limiting its use with other version control platforms.

Analysis

An editorial look at what each product does well and who it suits.

DeepSource
Dependabot

Overall verdict

  • DeepSource is a highly recommended tool for developers and teams looking to enhance their code quality and streamline code review processes. Its automated and insightful feedback helps prevent errors and improves overall software quality.

Why this product is good

  • DeepSource is often considered good because it provides automated code reviews, identifying issues related to code quality, security, and performance. It integrates seamlessly with various version control systems, offering ease of use and actionable suggestions to improve code. Additionally, it supports a wide range of programming languages and provides continuous analysis, making it a valuable tool for maintaining high code standards.

Recommended for

  • Software development teams
  • Individual developers
  • Organizations prioritizing code quality and security
  • Projects with multiple contributors
  • Teams using continuous integration and deployment pipelines

Overall verdict

  • Dependabot is a highly recommended tool for projects of any size that rely on external dependencies. It simplifies the update process, improves security, and integrates well with modern development workflows.

Why this product is good

  • Dependabot is considered a good tool because it automates the process of keeping dependencies up-to-date. It integrates seamlessly with platforms like GitHub, continuously monitors for dependency updates, and automatically creates pull requests for version bumps. This helps in enhancing security by ensuring that the project is using the latest versions of libraries, which may include important security patches. It also reduces the manual effort required for dependency management and allows developers to focus more on building features rather than maintenance tasks.

Recommended for

  • Projects that involve multiple dependencies and need regular updates.
  • Development teams aiming to automate routine maintenance tasks.
  • Organizations with a focus on enhancing security by keeping dependencies up-to-date.
  • Open-source projects that require streamlined version management.
  • Developers looking for a tool that's integrated with GitHub for enhanced collaboration.

Videos

Walkthroughs and reviews on video.

DeepSource 1 video + Add
Dependabot 0 videos + Add

How DeepSource works

No Dependabot videos yet. You could help us improve this page by suggesting one.

Category popularity

How often each product is chosen within a category, 0–100% relative to the other.

Score bands 0–20 21–40 41–50 51–60 61–100
DeepSource
Dependabot
74% 74%
26% 26%
0% 0%
100% 100%
100% 100%
0% 0%
0% 0%
100% 100%

User comments

Share your experience with using DeepSource and Dependabot. For example, how are they different and which one is better?

Log in or Post with

Reviews and articles

External articles and on-site reviews we used to compare the two products.

DeepSource no reviews yet
Dependabot no reviews yet
  • Top 11 SonarQube Alternatives in 2024
    www.codeant.ai · Oct 2024

    DeepSource, a comprehensive code review tool, offers detailed insights into code quality, security vulnerabilities, and productivity metrics. It empowers developers to identify and address potential issues early in...

  • The 5 Best SonarQube Alternatives in 2024
    blog.codacy.com · May 2024

    DeepSource’s focus on reducing false positives and providing actionable insights could make it an attractive option for teams looking to improve their code review process and overall code health. But while DeepSource...

Social recommendations and mentions

Recommendations tracked on public social media and blogs since March 2021.

DeepSource 16 mentions
Dependabot 14 mentions
  • DeepSource GitHub Integration: Setup and Configuration Guide
    Navigate to deepsource.com in your browser. - Source: dev.to / 6 months ago
  • Show HN: Autofix Bot – Hybrid static analysis and AI code review agent
    On the OpenSSF CVE Benchmark[1], Semgrep CE hits 56.97% accuracy vs our 81.21%, and nearly 3x higher recall (75.61% vs 26.83%). On when to run it, fair point. Autofix Bot is currently meant for local use (TUI, Claude Code plugin, MCP).... - Source: Hacker News / 9 months ago
  • How GraalVM improves Ruby
    Recently, there was a Java meetup held at work (Deepsource) where I gave my first ever talk, "How GraalVM improves Ruby". - Source: dev.to / over 3 years ago

View more

  • Automating Node.js Dependency Upgrades and Build Error Resolution Using AI
    Additionally, while tools like Dependabot already automate dependency updates, this solution offers something a bit different: it doesn’t stop at upgrading libraries—it helps you deal with the consequences of those upgrades by offering... - Source: dev.to / over 1 year ago
  • Be Secure and Compliant with GitHub
    GitHub integrated security scanning for vulnerabilities in their repositories. When they find a vulnerability that is solved in a newer version, they file a Pull Request with the suggested fix. This is done by a tool called Dependabot. - Source: dev.to / about 4 years ago
  • How to configure Dependabot with Gradle
    Dependabot provides a way to keep your dependencies up to date. Depending on the configuration, it checks your dependency files for outdated dependencies and opens PRs individually. Then based on requirement PRs can be reviewed and merged. - Source: dev.to / almost 5 years ago

View more

Alternatives to DeepSource and Dependabot

When comparing DeepSource and Dependabot, you can also consider the following products.