Security CI
The best Security CI Products based on votes, our collection of reviews, verified products and a total of 11 factors.


Best Security CI Products in 2026
Filter
Related categories
Popular features
-
 /snyk-alternatives
Snyk helps you use open source and stay secure. Continuously find and fix vulnerabilities for npm, Maven, NuGet, RubyGems, PyPI and much more.
Key Snyk features:
Ease of Use Comprehensive Vulnerability Database Automated Fixes CI/CD Integration
-
 Try for free
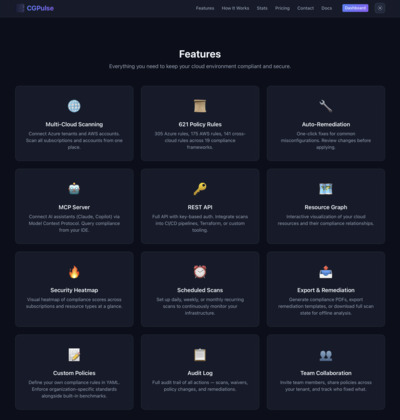
Scan Azure and AWS resources against 621 policy rules. Auto-remediate findings, track compliance frameworks, integrate via API.
-
 /qualys-alternatives
Qualys helps your business automate the full spectrum of auditing, compliance and protection of your IT systems and web applications.
Key Qualys features:
Comprehensive Security Cloud-based Platform Automated Scanning Detailed Reporting
-
 /sonarqube-alternatives
SonarQube, a core component of the Sonar solution, is an open source, self-managed tool that systematically helps developers and organizations deliver Clean Code.
Key SonarQube features:
Comprehensive code analysis Multi-language support Continuous integration (CI) integration Customizable rules
-
 /yara4pentesters-alternatives
rules to identify files containing juicy information like usernames, passwords etc - DiabloHorn/yara4pentesters.
-
 /whitesource-alternatives
Find & fix security and compliance issues in open source libraries in real-time.
Key WhiteSource features:
WhiteSource Core WhiteSource Priortize WhiteSource for Developers
-
 /yelp-s-detect-secrets-alternatives
detect-secrets is an aptly named module for (surprise, surprise) detecting secrets within a code base.
Key Yelp's detect-secrets features:
Open Source Prevent Secrets Leakage Customizable Plugins Extensible
-
 /repo-supervisor-alternatives
It happens sometimes that you can commit secrets or passwords to your repository by accident. The recommended best practice is not commit the secrets, that's obvious. But not always that obvious when you have a big merge waiting to be reviewed.
Key Repo-supervisor features:
Security Enhancement Automated Scanning Easy Integration Open Source
-
 /repo-security-scanner-alternatives
CLI tool that finds secrets accidentally committed to a git repo, eg passwords, private keys - UKHomeOffice/repo-security-scanner.
Key repo-security-scanner features:
Comprehensive Scanning Open Source Automation Ease of Use
-
 /nullify-ai-alternatives
Secure everything you build and run in your codebase.
-
 /cremit-alternatives
Effortless Non-Human Identity Security with Cremit.
Key Cremit features:
User-Friendly Interface Comprehensive Reporting Automation Features
-
 /arkin-alternatives
Software-defined data center operations platform.
Key Arkin features:
Comprehensive Network Visibility VMware Integration Micro-Segmentation Support Automated Network Analytics
-
 /vulmon-alerts-alternatives
Vulmon Alerts provides vulnerability notification service. Vulmon Alerts is how you proactively detect vulnerabilities. Subscribe to any query related to vulnerabilities and get alerted before hackers.
Key Vulmon Alerts features:
Comprehensive Coverage Timely Updates User-friendly Interface Customizable Alerts
-
 /gitrob-alternatives
Command line tool that finds sensitive information in your GitHub repositories.
Key Gitrob features:
Open Source Sensitive Data Detection Automation Integration with GitHub